Sector | HealthcareSecure Remote Access for Hospitals and Clinical Systems
Give medical device vendors and IT teams approved, recorded access to clinical and hospital systems, without a VPN, and keep the audit trail regulators ask for.
From IIJ, Japan's first internet service provider · Up and running in under 10 minutes · 24x7 support in English and Japanese
What Is Secure Remote Access for Healthcare?
It lets medical device vendors and hospital IT teams maintain clinical and hospital systems remotely while protecting patient data. Each user reaches only the approved system, access is approved and time-limited, credentials are never shared, and every session is recorded for regulators and internal audits.

Why Healthcare Needs Controlled Remote Access
Hospitals and clinics depend on outside vendors and small IT teams to keep clinical systems running. Every remote session into those systems is a path to patient data, so it needs to be approved, limited and recorded.
Vendors service medical systems
Imaging, lab and hospital information systems are often maintained remotely by their suppliers, frequently over VPNs and shared accounts.
Small IT teams, many systems
Lean IT teams look after clinical, administrative and building systems. They need control that does not add agents or network changes.
Regulators expect evidence
Healthcare is treated as critical infrastructure in several APAC countries. You need to show who accessed which system, when and why.
How Safous Secures Clinical and Hospital Systems
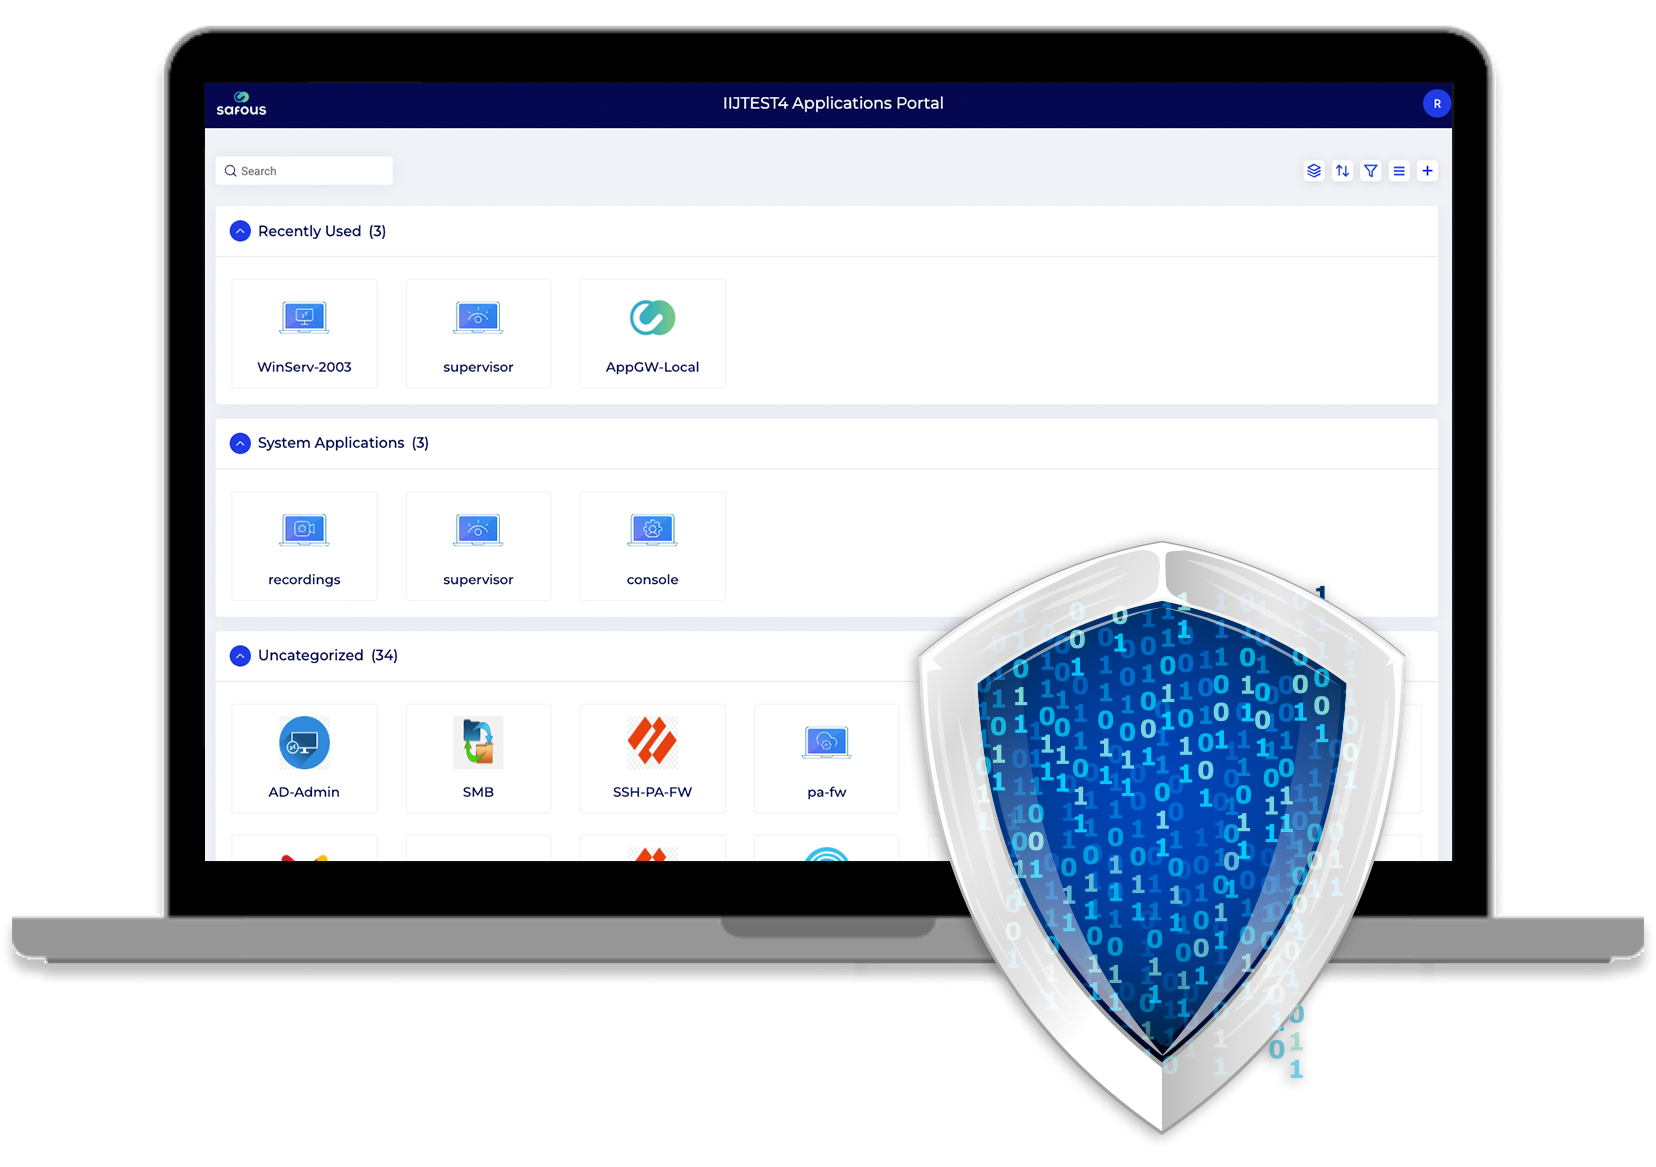
Safous connects a verified user to one approved system, not to your hospital network.
Just-in-time vendor access
Device and system vendors request access to the system they support. You approve it, and access ends when the work is done.
Agentless, browser-based
Connect over RDP, SSH, VNC and web from a browser. Nothing is installed on clinical systems or medical devices.
Vaulted credentials
Passwords are injected into the session and never shown, so vendors never share or keep admin accounts.
Recorded, audit-ready sessions
Watch sessions live, end them if needed, and keep recordings and logs for audits.
Credentials, logs and recordings stay in your own network on the Safous AppGateway. See third-party access →
See Safous on Your Clinical Systems
Book a demo or run a proof of concept in your hospital environment.

Ready for Healthcare Regulations in APAC
Safous provides the access controls and audit trails these rules ask for.
Thailand
Healthcare organizations designated as critical information infrastructure under the Cybersecurity Act must control and monitor access to critical systems.
Singapore
Healthcare is a critical information infrastructure sector. CII owners must meet the access-control and logging requirements in CCoP 2.0.
Malaysia
Healthcare services is a national critical information infrastructure sector under the Cyber Security Act 2024.
HIPAA
For organizations that handle US patient data, Safous supports HIPAA access-control and audit requirements.
Healthcare Resources
Guides and talks to help you plan secure remote access for clinical and hospital systems.
Regulatory Compliance & Audit
How Safous helps you meet access-control and audit requirements across APAC.
Read more →WebinarDigital Health Check-Up
Cybersecurity risks and remote access in healthcare.
Read more →BlogWhat’s Next for Healthcare Cybersecurity in APAC
Trends and threats shaping healthcare security across the region.
Read more →SolutionThird-Party & Vendor Access
Give vendors access to only the systems they maintain.
Read more →AssessmentExternal Attack Surface Assessment
See what attackers can see across your hospitals and suppliers.
Read more →AssessmentInternal Vulnerability Assessment
Find and prioritize vulnerabilities inside hospital networks.
Read more →Frequently Asked Questions
How does Safous protect patient data during remote access?
Safous connects a verified user to one approved application instead of the whole network. Access needs MFA and can require approval, credentials are injected without being shown, and every session is recorded. Credentials, logs and recordings stay in your own network on the Safous AppGateway.
Can medical device and system vendors connect without a VPN?
Yes. Vendors reach only the system they maintain through a browser, with just-in-time access that expires when the work is done. No VPN, no standing accounts and no shared passwords.
Does Safous support Thailand's cybersecurity requirements for healthcare?
Yes. Healthcare organizations designated as critical information infrastructure in Thailand must control and monitor access to critical systems. Safous provides the access controls and audit trails, and our Thailand NCSC checklist maps them to the requirements.
Does Safous help with HIPAA compliance?
Safous supports HIPAA access-control and audit requirements with unique user identities, MFA, least-privilege access, and logs and recordings of every privileged session. It is one part of a HIPAA program, not a certification on its own.
Do we need to install agents on clinical systems?
No. Safous is agentless. Users connect over RDP, SSH, VNC or web from a browser, so nothing is installed on clinical or medical systems.
See Safous on Your Own Systems
Book a demo, or run a proof of concept in your own environment.
