OT Secure Remote Access for Industrial Environments
Safous gives engineers, integrators and machine builders controlled access to OT and ICS assets from anywhere. Every session is approved, recorded and limited to the asset the user needs, with no VPN and no client install.
What Is OT Secure Remote Access?
OT secure remote access controls how engineers, OEMs and system integrators connect to industrial systems such as PLCs, HMIs and SCADA from outside the plant. Instead of a VPN that opens the control network, each user reaches only the approved asset after MFA and approval, and every session is recorded. Safous delivers this without agents, including for isolated and air-gapped sites.
Why industrial remote access needs its own controls
Plants now depend on remote support from OEMs, system integrators and central engineering teams. VPNs and shared jump servers give those users a path to the whole network and leave little record of what they did. In OT, one wrong command can stop a line, so access must be narrow, supervised and fully logged.
How Safous Secures OT Remote Access
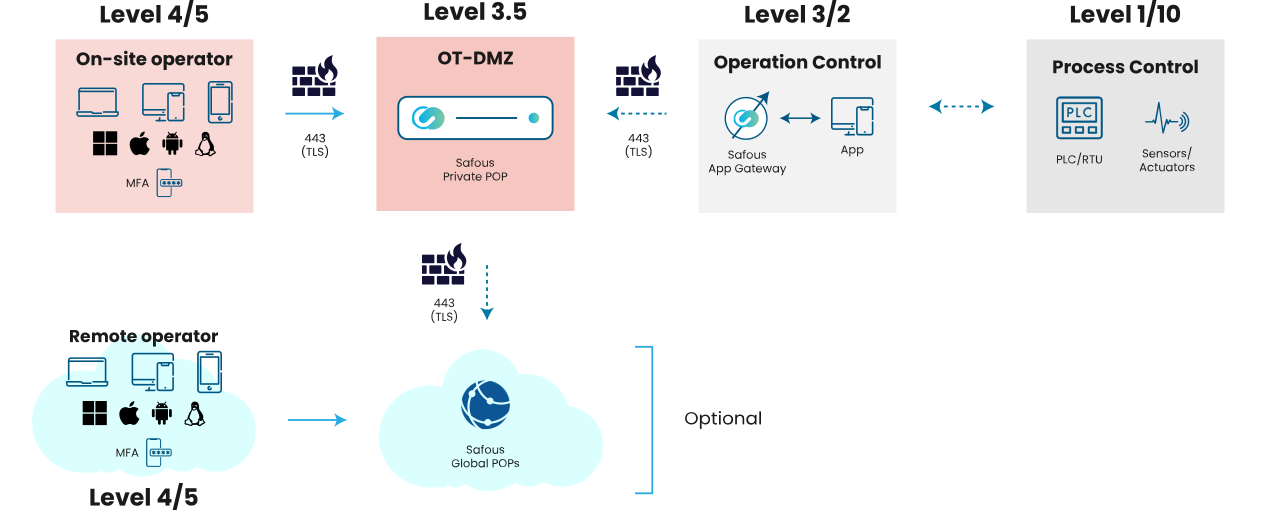
Engineers, OEMs and integrators reach one approved asset through the Safous AppGateway in your network, never the plant network itself.
Architecture
What Safous provides
- Asset-level access, not network access: users reach only the PLC, HMI, engineering workstation or web app they are allowed to use.
- Agentless protocols: RDP, SSH, VNC, Telnet, web apps and SMB file shares from a browser, plus agent-based access for other TCP/UDP protocols.
- Supervised sessions: supervisor approval for sensitive assets, approvals of up to five stages, and live monitoring with the option to end a session.
- Session recording and command logs: browser playback, keyword search across commands, and SSH command control.
- No shared passwords: vaulted credentials are injected into the session, with just-in-time, time-limited access.
- Safe file transfer: file scanning, including ICAP integration, and clipboard and file controls.
Safous vs. Other Ways to Reach OT Remotely
Why industrial remote access needs more than a VPN or a remote desktop tool.
| VPN | Jump server | Remote desktop tools | Safous | |
|---|---|---|---|---|
| What users reach | The control network | A shared host on the network | The machine running the agent | One approved asset |
| OEM and vendor control | Shared VPN accounts | Shared accounts | Hard to govern centrally | Per-vendor, time-bound, with approvals |
| Session recording | No | Rarely | Varies | Yes, with live supervision and termination |
| Software on OT systems | VPN client on laptops | Remote desktop client | Agent on the target host | Nothing on OT assets |
| Air-gapped sites | Not supported | Possible, manual | Not supported | Isolated AppGateway supported |
| Evidence for ISA/IEC 62443 | Limited | Partial | Limited | Approvals, recordings and logs |
Built for isolated and air-gapped sites
The Safous AppGateway runs inside your environment on a server, a virtual machine or in the cloud. For sites that must stay offline, an isolated AppGateway supports air-gapped environments, and a private PoP keeps data in your region. This lets you place access controls between the enterprise network and the control network, in line with zone-and-conduit designs.
Supports OT security standards
Recorded, approved and least-privilege access maps to common requirements in ISA/IEC 62443, NIST CSF and national frameworks across APAC. See the ISA/IEC 62443 compliance checklist and the ASEAN cybersecurity checklist.
By industry
Manufacturing · Automotive · Energy and utilities · Critical infrastructure · Maritime · Mining · Pharma and life sciences · Food and beverage
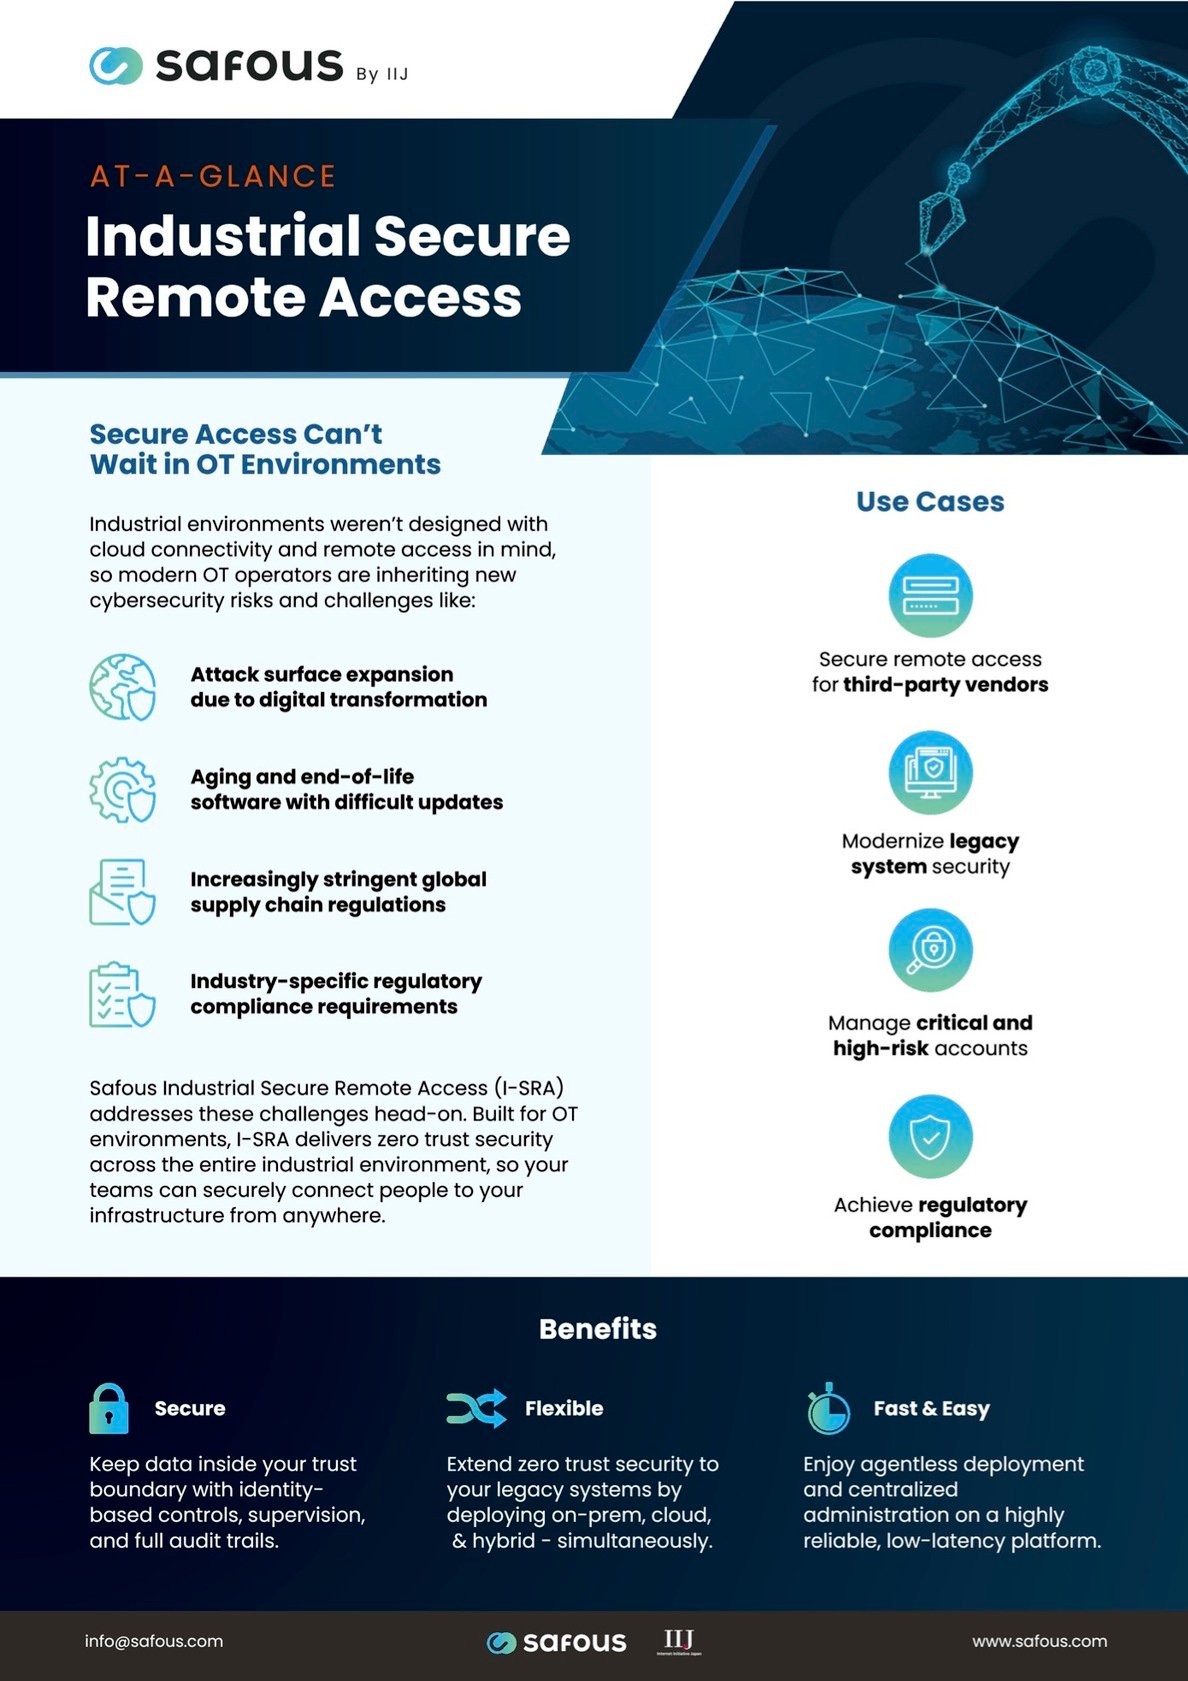
Industrial Secure Remote Access At-A-Glance
A two-page overview of how Safous secures remote access to OT and industrial systems, including isolated and air-gapped sites.
Customer Stories
How industrial organizations secure OT and vendor access with Safous.
Global automaker
Challenge: Across more than 10 production sites, IT remote access tools did not work with OT systems, and agents could not be installed on OT assets.
Result: Agentless, fully audited OT access replaced the VPN and aligned IT security with plant operations.
Global food manufacturer
Challenge: OEMs and contractors needed seven logins to reach one machine over VPN.
Result: One browser-based portal for employees, contractors and OEMs across 150 sites, rolled out in under 90 days.
Maritime operator
Challenge: Remote maintenance of lighthouses, offshore plants and port facilities relied on a vulnerable access tool.
Result: Secure, stable remote maintenance for 200 lighthouses, 250 offshore plants and 1,000 port facilities.
See Safous on Your Own OT Systems
Book a demo or run a proof of concept at one of your sites.
Frequently Asked Questions
What is OT secure remote access?
It is controlled remote access to operational technology such as PLCs, HMIs and SCADA. Each user reaches only approved assets, and every session is authenticated, supervised and recorded.
Does Safous need a VPN or a client on the engineer's laptop?
No. Users connect through a web portal with no client and no VPN. Agent-based access is available for other TCP/UDP protocols.
Can Safous work in air-gapped environments?
Yes. An isolated Safous AppGateway supports air-gapped sites, and a private PoP keeps data in your region.
How do we let OEMs support our machines safely?
Give each vendor access to its own equipment only, require supervisor approval, and record the session. Access ends when the job is done.
Which protocols are supported?
RDP, SSH, VNC, Telnet, web apps and SMB agentlessly, plus any TCP/UDP protocol with the agent.
Related: Third-party and vendor access · Privileged remote access guide · Safous Privileged Remote Access at a glance
More Resources

Agentless Remote Access for IT, OT and IoT: How It Works and When to Use It
Managing Supply Chain Cyber Risk: A CISO’s Guide to Operational Resilience