Check out our new resource center! Get compliance docs! Explore the resource center
Product/Services

Product

Custom Solutions

Security Assessment Services

Solutions

Solutions

Safous offers advanced cybersecurity solutions for modern use cases and multiple industries.

Use Cases

Industries

Partners

Partners

Partner with Safous to offer your clients the security they're looking for – and take hold of a piece of a growing market. 

Safous Partner Program

Provide your clients with the advanced cybersecurity they need.

MSPs / SI / Whitelabel

Protect your clients from cyberattacks and unlock your growth.
Resources

Content Library

Visit our content library to view the latest updates in cybersecurity, Privilege and Remote Access, and protecting your digital assets.

Docs

Find comprehensive guides and documentation to help you get started with Safous, plus support if you get stuck.

Latest Events

Company

About Us

We’re focused on helping people access the corporate resources they need to get their jobs done safely, comfortably, and easily. That’s why our motto is Safe for You and Us.

Compliance

Find all Safous compliance & security info in one place — certifications, policies, and audit details.

ProductSafous Privileged Remote Access

One platform to approve, broker, monitor and record every privileged session to IT, OT and IoT systems, for admins, engineers, vendors and AI agents. No VPN, no agents, and your data stays in your network.

From IIJ, Japan's first internet service provider · Up and running in under 10 minutes · 24x7 support in English and Japanese

What Is Safous Privileged Remote Access?

Safous Privileged Remote Access (PRA) is a remote privileged access management (RPAM) platform from IIJ. It lets administrators, engineers, third-party vendors and AI agents securely connect to critical systems with just-in-time access to one approved IT, OT or IoT system at a time, from a browser, without a VPN or agents. Every session is approved, monitored in real time and recorded, and credentials stay vaulted in your own network.

How Safous Works

Safous connects a verified identity to one approved application, never to your network.

Safous combines IAM, Zero Trust and PAM to connect IT administrators, OT operators, third-party vendors and AI agents to servers, web apps, OT and IoT devices and cloud systems
1

Verify

Users sign in with SSO and MFA through your identity provider, such as Microsoft Entra ID.

2

Approve

Policies decide who can reach which system and when. Sensitive access can require just-in-time approval.

3

Connect

The Safous AppGateway brokers the session to one application and injects vaulted credentials.

4

Record

Sessions are monitored live, can be terminated, and are recorded with full audit logs.

See It in 90 Seconds

Verify, Approve, Connect and Record across IT, OT and third-party vendors, plus deployment options and supported protocols.

Watch the Safous overview on YouTube

Watch with chapters and transcript

Everything You Need for Privileged Remote Access

Safous covers the core RPAM capabilities described by Gartner: policy-based access, privileged session security, and integrated MFA and vaulting.

Identity-based access

SSO and MFA before every session, with policies down to the user, application and time window, enforcing least privilege for every account.

Just-in-time approvals

Grant time-bound access on request and remove it automatically when the work is done.

Credential vaulting

Passwords are injected into sessions and never shown, so no one shares or keeps admin accounts.

Session monitoring and recording

Watch sessions in real time, end them when needed, and keep recordings for audits and investigations.

Agentless browser access

RDP, SSH, VNC and web access from a browser, with nothing installed on target systems.

Audit logs and reporting

Every login, approval and session is logged so you can show auditors who did what, when.

Privileged Remote Access Security Controls in Detail

Privileged remote access (PRA) works best when several controls stack on every session. Here is how Safous applies each one, from the first login to the audit report.

Identity and MFA first

Every user signs in through SSO with your IdP or the Safous IdP. MFA by TOTP, email, SMS or WhatsApp is checked before any session starts.

Enforcing least privilege per application

Policies grant access to a single application or system, not a whole network. Users see only what their role allows, so a stolen account cannot roam.

Just-in-time and temporary access

Access opens for a set time window and closes on its own. For a quick vendor session, you can issue temporary, single-use access instead of creating a standing account.

Multi-stage approvals

Route requests through up to five approval stages. A plant manager and a security lead can both sign off before anyone can connect to critical systems.

Credential injection

Safous injects vaulted credentials into the session, so passwords are never shown. Securely managing admin accounts no longer depends on sharing them by email or chat.

Live monitoring and termination

Security teams can watch any session in real time. If something looks wrong, they can end the session immediately.

Recording and command-level logs

Every session is recorded, with command-level logs. You can replay exactly what happened on a server or controller.

Audit-ready evidence

Logins, approvals, sessions and recordings are kept together. When auditors ask who accessed a system and why, the answer is already on file.

Privileged Remote Access
Purpose-Built for Real-World Security

Safous simplifies secure access for IT, OT, and third-party vendors, all while helping you check off compliance requirements from a single, modern platform.

Benefits

icon-RPAM-4-1
Fast, flexible deployment across IT, OT, and IoT
icon-RPAM-4-2
Easy remote access management for vendors and third parties Learn about third-party access
icon-RPAM-4-3
Align with GDPR, ISO 27001, NIST 800-171, and more
icon-RPAM-4-4
Eliminate the need for multiple point solutions Learn about RPAM

Differentiators

icon-RPAM-4-5
Agentless architecture with granular policy enforcement
icon-RPAM-4-7
Integrated password vaulting and SSO support
icon-RPAM-4-8
Session visibility with recording, alerting, and JIT controls
icon-RPAM-4-9
RDP/SSH/VNC over browser with controls
icon-RPAM-4-10
Designed for hybrid infrastructure across APAC
icon-RPAM-4-11
Licensing that works for your team: named or concurrent
icon-RPAM-4-12
Deploy in any environment: on-prem, offline, or cloud-connected
icon-RPAM-4-13
Keep all sensitive data inside the customer’s trusted boundaries
Safous vs. VPN, Jump Servers and Traditional PAM

How remote privileged access compares across common approaches.

VPNJump serverTraditional PAMSafous
What users reachThe whole networkA shared host inside the networkCredentials, often still over VPNOne approved application
Third-party vendorsShared accounts and VPN clientsShared accountsPossible, but complex to set upBuilt in, time-bound, with approvals
Session recordingNoRarelyYesYes, with live monitoring and termination
CredentialsKnown to usersOften sharedVaultedVaulted and injected, never shown
Agents and clientsVPN client on every deviceRemote desktop clientAgents often requiredAgentless, from a browser
OT and isolated sitesRisky for OT networksLimitedLimitedBuilt for OT, including air-gapped sites
Time to deployDaysWeeksMonthsMinutes

How to Choose a Privileged Remote Access Solution

Most privileged remote access tools look alike on a feature list. The differences show up in daily use. Use these questions to compare options side by side.

  • Protocol coverage: Does it handle RDP, SSH, VNC, web apps and file transfer? Can it reach other TCP/UDP systems when needed?
  • Agentless access: Can users connect from a browser, with nothing to install on targets or laptops?
  • No inbound ports: Does it work without opening inbound firewall ports or exposing a VPN gateway?
  • OT and air-gapped support: Can it run on-premises or fully offline at isolated sites?
  • Deployment time: How long does a first connection take? Safous is up and running in under 10 minutes.
  • Licensing model: Does pricing fit how you work, with named-user or concurrent-user options for shifting vendor teams?
  • Audit evidence: Are recordings, command logs and approval history easy to export for audits?
  • Support: Is help available 24x7, in the languages your teams use? Safous offers support in English and Japanese.

The best test is a proof of concept on your own systems. It shows quickly whether a tool fits your network, your vendors and your audit needs.

Why Teams Trust Safous

From Japan's first ISP

Safous is provided by IIJ, Japan's first internet service provider and a Tokyo Stock Exchange Prime-listed company serving approximately 16,000 customer companies across the IIJ Group.

ISO/IEC 27001 and SOC 2

Safous is certified to ISO/IEC 27001 and audited for SOC 2.

24x7 support

Support is available around the clock in English and Japanese.

Proof of concept

Run Safous on your own systems before you buy.

Customer Stories

How organizations secure administrator, OT and vendor access with Safous.

Manufacturing · Japan

Toray Industries

Challenge: Administrator access to servers across a distributed group network was exposed to repeated break-in attempts.

Result: Administrator logins now go through Safous, with zero unauthorized admin logins.

Read the case study →

Food manufacturing · Global

Global food manufacturer

Challenge: OEMs and contractors needed seven logins to reach one machine over VPN.

Result: One browser-based portal for employees, contractors and OEMs across 150 sites, rolled out in under 90 days.

Maritime · Indonesia

Maritime operator

Challenge: Remote maintenance of lighthouses, offshore plants and port facilities relied on a vulnerable access tool.

Result: Secure, stable remote maintenance for 200 lighthouses, 250 offshore plants and 1,000 port facilities.

Built to Fit Your Network

Deploy Safous where your systems are, and keep sensitive data under your control.

Cloud-routed, not cloud-hosted

Credentials, logs and recordings stay on the Safous AppGateway in your network. No inbound firewall ports are needed.

Global PoPs

Safous runs through PoPs worldwide, with dense coverage across Asia and presence in North America and Europe. A private PoP is also available.

Deploy your way

Run Safous cloud-connected, on-premises or fully offline, including isolated and air-gapped OT sites.

Flexible licensing

Choose named-user or concurrent-user licensing to match how your teams and vendors work.

Try Safous on Your Own Systems

A proof of concept runs in your environment, with your users and your systems.

1

Scope

Pick one or two use cases, such as vendor access or admin access, and the systems to include.

2

Deploy

Install the Safous AppGateway in your network on a server or VM. It takes minutes.

3

Run real sessions

Admins and vendors connect through Safous. Approvals and recordings work from day one.

4

Review

Check the results with our engineers and plan the rollout.

Request a Demo or PoC

Who Uses Privileged Remote Access

Privileged remote access serves anyone who needs elevated access to systems they do not sit next to. Safous gives each group the same controls, tuned to their role.

IT administrators

Admins reach servers, databases and network devices from a browser. They work without a VPN, and every session is logged.

Third-party vendors and OEMs

Vendors get access to only the equipment they maintain, for only as long as the job takes. No shared passwords, no standing accounts.

OT engineers

Engineers connect to PLCs, HMIs and SCADA systems at remote plants. Approvals and recordings keep changes on the shop floor visible.

Managed service providers

MSPs manage many customer environments from one place. Each customer keeps its own policies, approvals and records.

Auditors and compliance teams

Reviewers check recordings, command logs and approval history to confirm that access followed policy.

AI agents under human approval

When AI agents need system access, Safous can place them behind human-in-the-loop approval with a full audit trail.
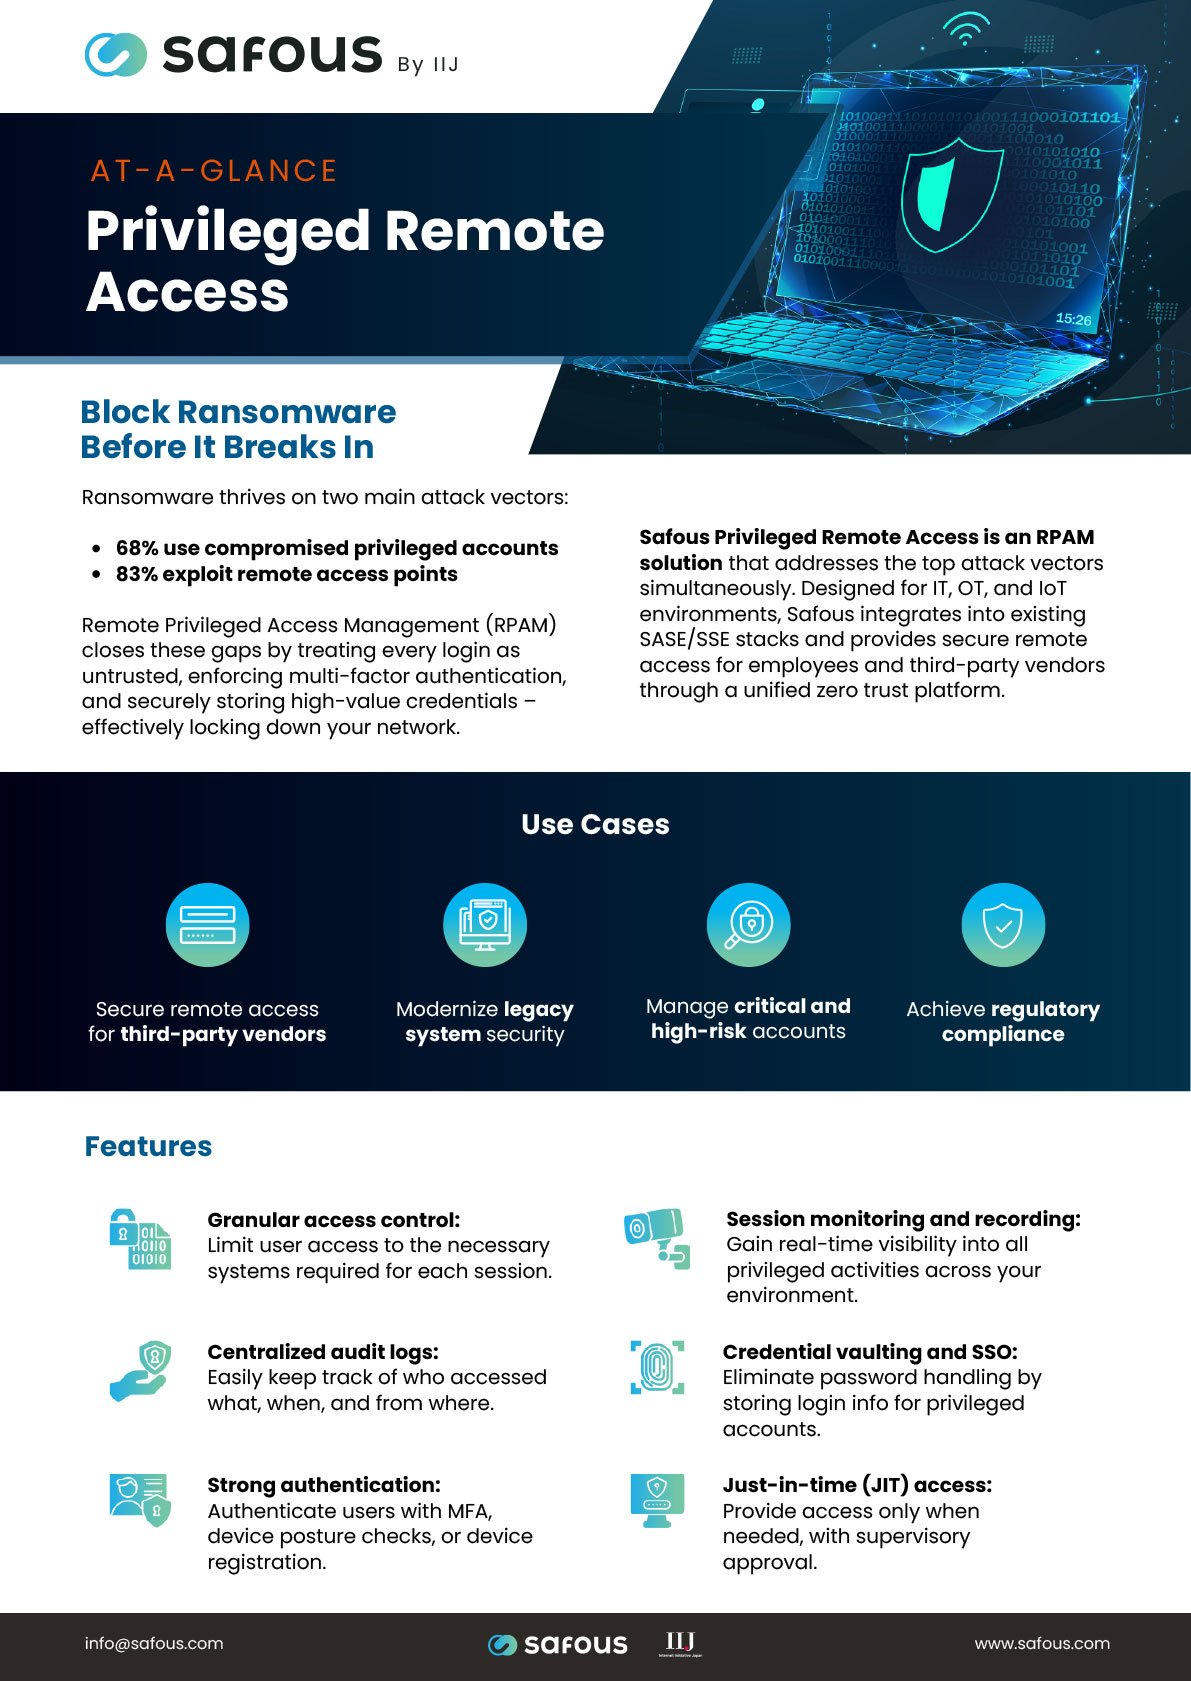
Safous-PRA-At-a-Glance-cover
At a Glance

Privileged Remote Access At-A-Glance

Discover how Remote Privileged Access Management (RPAM) closes these gaps by treating every login as untrusted, enforcing multi-factor authentication. 

Frequently Asked Questions

What is Safous Privileged Remote Access?

Safous Privileged Remote Access is a remote privileged access management (RPAM) platform from IIJ, Japan's first internet service provider. It gives administrators, engineers, third-party vendors and AI agents just-in-time, recorded access to specific IT, OT and IoT systems without a VPN.

How does Safous work?

Users sign in to the Safous portal with SSO and MFA. After policy checks and any required approval, Safous routes the session through its PoPs to the Safous AppGateway in your network, which connects the user to the one approved application. There are no agents on target systems and no inbound firewall ports.

Which protocols and systems does Safous support?

Safous supports RDP, SSH, VNC and web applications in the browser, as well as databases and file shares, across servers, cloud workloads, OT systems such as PLCs, HMIs and SCADA, and IoT devices.

Can Safous run on-premises or in an offline environment?

Yes. Safous can be deployed cloud-connected, on-premises or fully offline, including isolated and air-gapped sites. A private PoP is also available.

How is Safous licensed?

Safous offers named-user or concurrent-user licensing, so you can match the license to how your admins and vendors actually work.

Can we try Safous before buying?

Yes. You can book a demo or run a proof of concept in your own environment.

What is privileged remote access (PRA)?

Privileged remote access (PRA) is the practice of securely managing remote connections from administrators, engineers and vendors to critical and sensitive systems. A PRA solution verifies each user's identity, enforces least privilege, and monitors and records every privileged session.

How does Safous secure vendor remote access?

Vendors sign in with SSO and MFA and reach only the systems they maintain, for an approved time window. Credentials are injected and never shown, and every vendor session is monitored in real time and recorded. There are no shared accounts, VPN clients or agents to manage.

Can Safous control access by AI agents?

Yes. AI agents connect through Safous like any other privileged user. You can require human approval before each session, limit the agent to specific applications, and record every session.

home-1-1

See Safous on Your Own Systems

Book a demo, or run a proof of concept in your own environment.