





The best privileged access management for third-party access does two jobs. It protects privileged credentials. It also controls the vendor’s whole access path, from identity checks and approval to session oversight and termination.
A secure password vault matters. But a vault alone does not decide if an outside technician should connect today. It does not limit which systems they reach or when their access ends.
Many organizations work with equipment vendors, maintenance contractors, system integrators, and external support teams. For them, the buying decision should start with these access needs. That is where remote privileged access management comes in.
This guide covers three things. It explains what a credential-focused PAM setup can miss. It shows where PAM and Privileged Remote Access (PRA) fit. And it shows how to test seven solutions against real vendor workflows.
What Is Privileged Access Management?
Privileged access management (PAM) is the practice of controlling and monitoring elevated access to sensitive systems, apps, and data. PAM tools can offer credential vaulting, password rotation, approval workflows, privileged session management, and related controls.
Third-party access is a wider use case. It includes privileged work, such as running a server. It can also include non-admin work, such as viewing a maintenance app.
You need to govern both. A vendor’s permissions should match the approved task, whether or not that task needs a privileged account.
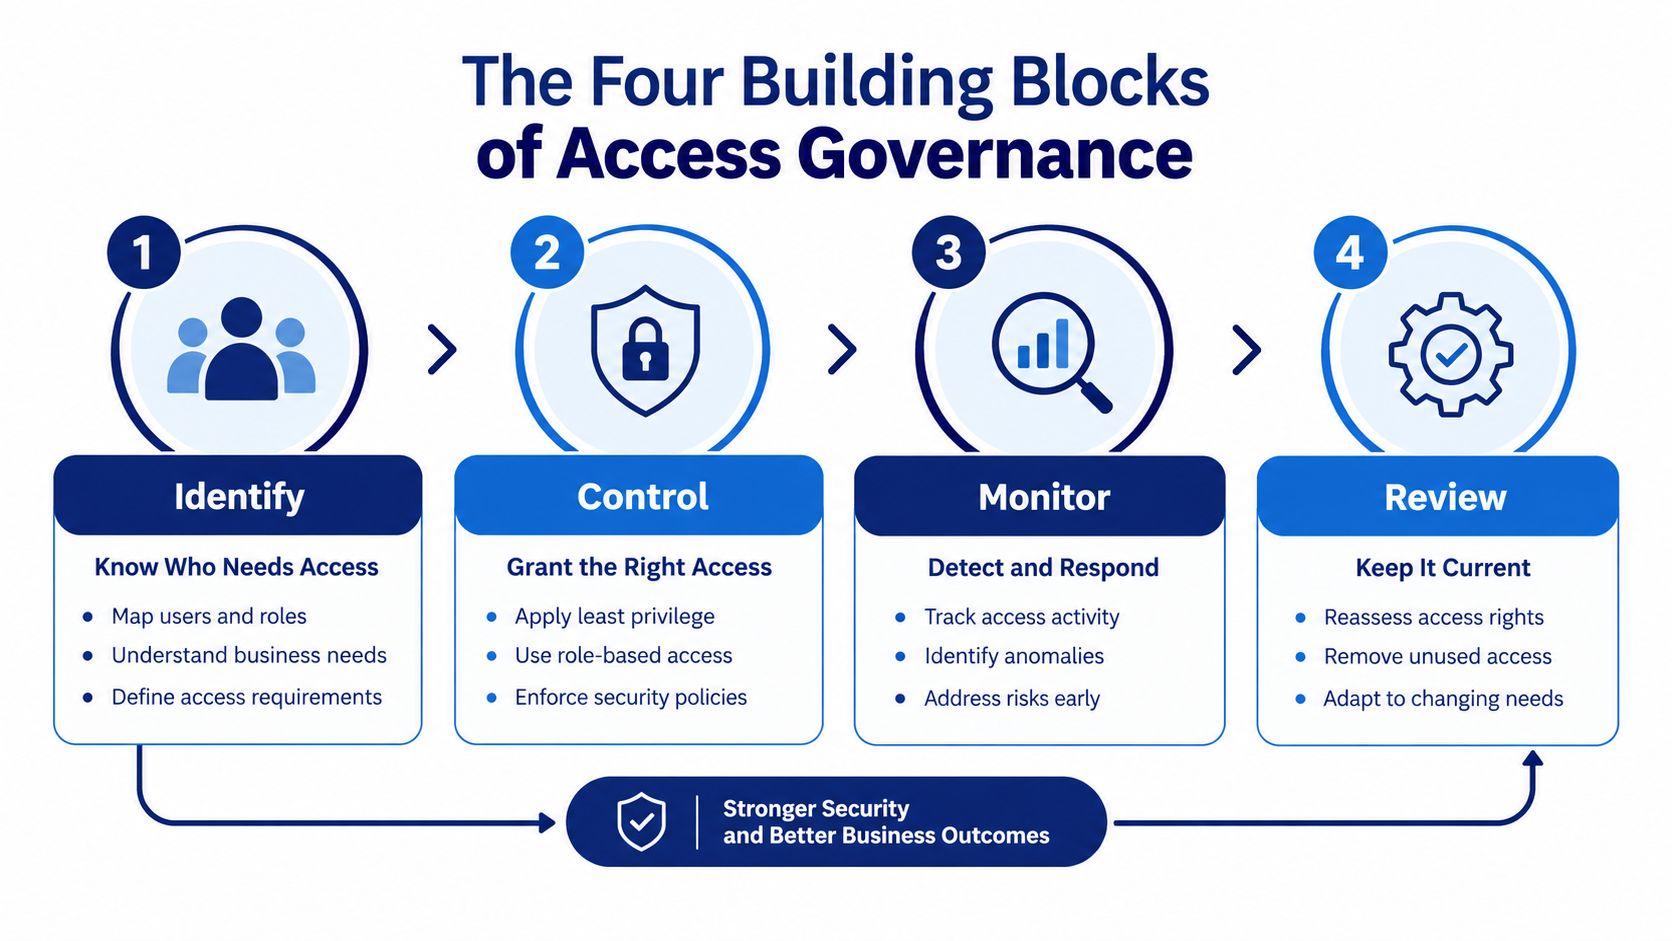
For the governance basics, see What Is Access Governance? Why Third-Party Access Needs a Different Model.
What Is the Difference Between PAM and PRA?
PAM covers privileged access across the whole organization. Privileged Remote Access (PRA) focuses on how remote users reach and use sensitive resources.
Remote Privileged Access Management (RPAM) is another term. It refers to managing the full lifecycle of remote privileged connections. Vendors use these terms in different ways, and the lines between them vary.
One PAM platform may already include remote vendor access controls. Another may need extra components or integrations.
So the real question is not whether a product says PAM or PRA. It is whether the deployed solution controls the vendor’s identity, permissions, connection, activity, and access expiry.
What Can Traditional PAM Miss in Third-Party Access?
A PAM setup that focuses mainly on protecting credentials can leave gaps. These gaps show up in vendor onboarding, resource access, session oversight, and timely revocation.
This does not mean modern PAM platforms lack these features. Many offer dedicated vendor access functions. The risk is assuming that your current vault or internal admin workflow covers outside users by default.
1. Individual Accountability Beyond a Shared Account
A target system may need a shared admin account. You should still be able to identify the vendor technician who used it.
A log entry that says “vendor-admin” logged in may not be enough. It may not show who did the work, which supplier they worked for, or who approved the session.
Check whether the solution links each outside user to an accountable internal owner. It should also keep that identity in the access record from start to finish.
2. Access from Devices Outside Your Management
Vendors often connect from devices their own employer manages, not yours. Your internal admin workflows may rely on endpoint agents, corporate directories, or device controls. Those users may not have any of them.
Browser-based or agentless access can cut down on software installs. But it does not make an unmanaged device trustworthy. It also does not remove endpoint risk.
Test the access method, login requirements, supported protocols, and file or clipboard controls against the devices your vendors really use.
3. A Controlled Path to the Required Resource
Protecting a password does not limit what the user can reach once connected.
If the vendor’s connection opens more of the network than needed, credential controls alone may still let them reach unrelated systems.
Check whether the access path limits the vendor to the approved app or asset. Then confirm how your environment enforces that limit.
4. Task-Based Approval and Access Duration
An active support contract does not justify open access for the whole contract term.
For work that comes and goes, link approval to a task, ticket, or maintenance window. Temporary permissions should expire as the policy states. Just-in-time (JIT) access, granted for a time-bound window, keeps a vendor's privileges from outliving the task.
Also tell apart blocking a new connection and ending an active session. A solution should show the right behavior for both.
5. Oversight During the Session
Password checkout records show that a credential was handed out. They do not show what happened on the target system.
Sensitive vendor work may need session monitoring, recording, supervision, or intervention. The right controls depend on the system, access method, and operational risk. Real-time monitoring helps teams spot suspicious activity while a session is still in progress.
Check which session types are supported. Also check whether the evidence is useful to both security teams and system owners.
6. Compatibility with IT and OT Operations
Vendor support often reaches systems that are not like standard office IT. Examples include legacy apps, engineering workstations, industrial assets, and sites with limited connectivity.
A smooth RDP demo does not prove the tool works with every OT workflow.
Check the real access route, protocol support, login limits, maintenance steps, and recovery behavior. In isolated sites, review the approved connectivity design. Do not assume normal remote access will work there.
Where Do PAM, PRA, ZTNA, and SASE Fit?
Secure third-party access is the goal. PAM, PRA, ZTNA, and SASE are tools that can help you get there.
These categories overlap. A single product can span several of them.
You do not have to pick just one. An organization may keep its PAM vault, use ZTNA for app access, and add PRA for sensitive vendor sessions.
The goal is to cover the whole workflow with clear owners and controls you can enforce.
Seven PAM and PRA Solutions to Evaluate for Third-Party Access
The solutions below offer relevant privileged access features. This is a shortlist based on requirements. It is not a ranking, and it is not based on side-by-side performance tests.
Features depend on the product, edition, deployment, integration, and configuration. Test the exact combination proposed to you. Do not treat a vendor’s whole portfolio as one package.
Safous Privileged Remote Access
Safous Privileged Remote Access focuses on controlled access to IT and OT applications. Session recording and access request and approval workflows are included as standard. It also offers policy-based access, built-in MFA, credential vaulting, and privileged session supervision and termination.
Safous also supports agentless access for unmanaged users and devices. This meets a common third-party access requirement.
What to test: Check the standard request, approval, and recording workflow, from vendor request to expiry and evidence retrieval. Test browser-based access, session supervision and termination, and Safous AppGateway deployment in your IT/OT environment.
CyberArk / Idira Privileged Access Management
The PAM page linked from CyberArk’s product page highlights Idira capabilities, including credential vaulting and rotation, session isolation, and browser-based, just-in-time access for external contractors.
This shows why modern PAM should not be judged only as password storage. Vendor access and session controls can be part of a wider privileged access offering.
What to test: Confirm which modules and licenses cover vaulting, vendor access, approval, recording, and just-in-time authorization. Test the full workflow across those components to find integration gaps.
BeyondTrust Password Safe and Privileged Remote Access
BeyondTrust Privileged Remote Access provides capabilities for controlling remote privileged sessions, including credential injection. Password Safe provides dedicated credential, secrets, and session management capabilities.
Credential injection can reduce the need for users to handle target passwords directly. Buyers should still check how the proposed products work together.
What to test: Confirm client and gateway requirements for each access method. Confirm which features need Password Safe or other products. Test credential injection, session controls, and recording/search, especially on OT targets that cannot accept agents.
Delinea Secret Server and Related Privilege Controls
Delinea Secret Server lists approval workflows, session recording, monitoring, and RDP/SSH proxying among its capabilities. Features vary by edition and additional services.
Endpoint privilege management covers a related need: controlling privileges on endpoints. Assess it apart from the outside vendor’s connection to a target system.
What to test: Confirm product, edition, and add-on needs, especially for advanced recording, search, and agent deployment. Test the vendor workflow across products. Where required, check that it works without cloud connectivity.
One Identity Safeguard
One Identity Safeguard includes privileged password and session management offerings. Safeguard Remote Access provides a remote access path and integrates with Safeguard for Privileged Sessions.
What to test: Check how the remote access, password management, and session management parts work together. Confirm that identity, approval, credential use, recording, and revocation stay traceable for the whole vendor session.
ManageEngine PAM360
ManageEngine PAM360 presents a unified PAM platform with capabilities for privileged identities and remote access workflows for vendors and third parties.
What to test: Check external vendor workflows, including gateway and directory dependencies and any user-side installs. Also check how evidence is gathered in one place, how it handles limited OT connectivity, and the ongoing admin effort.
WALLIX PAM / Bastion
WALLIX PAM presents privileged account and session management capabilities, including credential vaulting and rotation, session recording, and agentless controls across IT and OT environments.
What to test: Confirm the components and licenses needed for remote access, approval, recording, and search. Include operation at disconnected sites. Test evidence correlation and, where required, endpoint privilege controls or industrial-protocol tunneling.
PAM Solutions Comparison for Third-Party Access
Use this comparison to decide what to check in a proof of concept. It does not give universal scores for cost, complexity, or security results.
Sources are the official product pages linked above. Confirm current packaging and features directly with each provider.
How to Choose the Best Remote Privileged Access Management Solution for Third-Party Access
Start with typical vendor tasks. Identify the controls each task needs. Then test the full workflow before you compare commercial offers.
A feature checklist helps. But it should describe behavior you can observe, not broad labels such as “Zero Trust” or “OT support.”
Build a Requirements Scorecard
Treat must-have controls as pass/fail. Use weighted scores for other differences, such as ease of use, integration effort, and operating cost.
Test a Complete Vendor Session
A useful proof of concept follows the vendor’s work from request to closure:
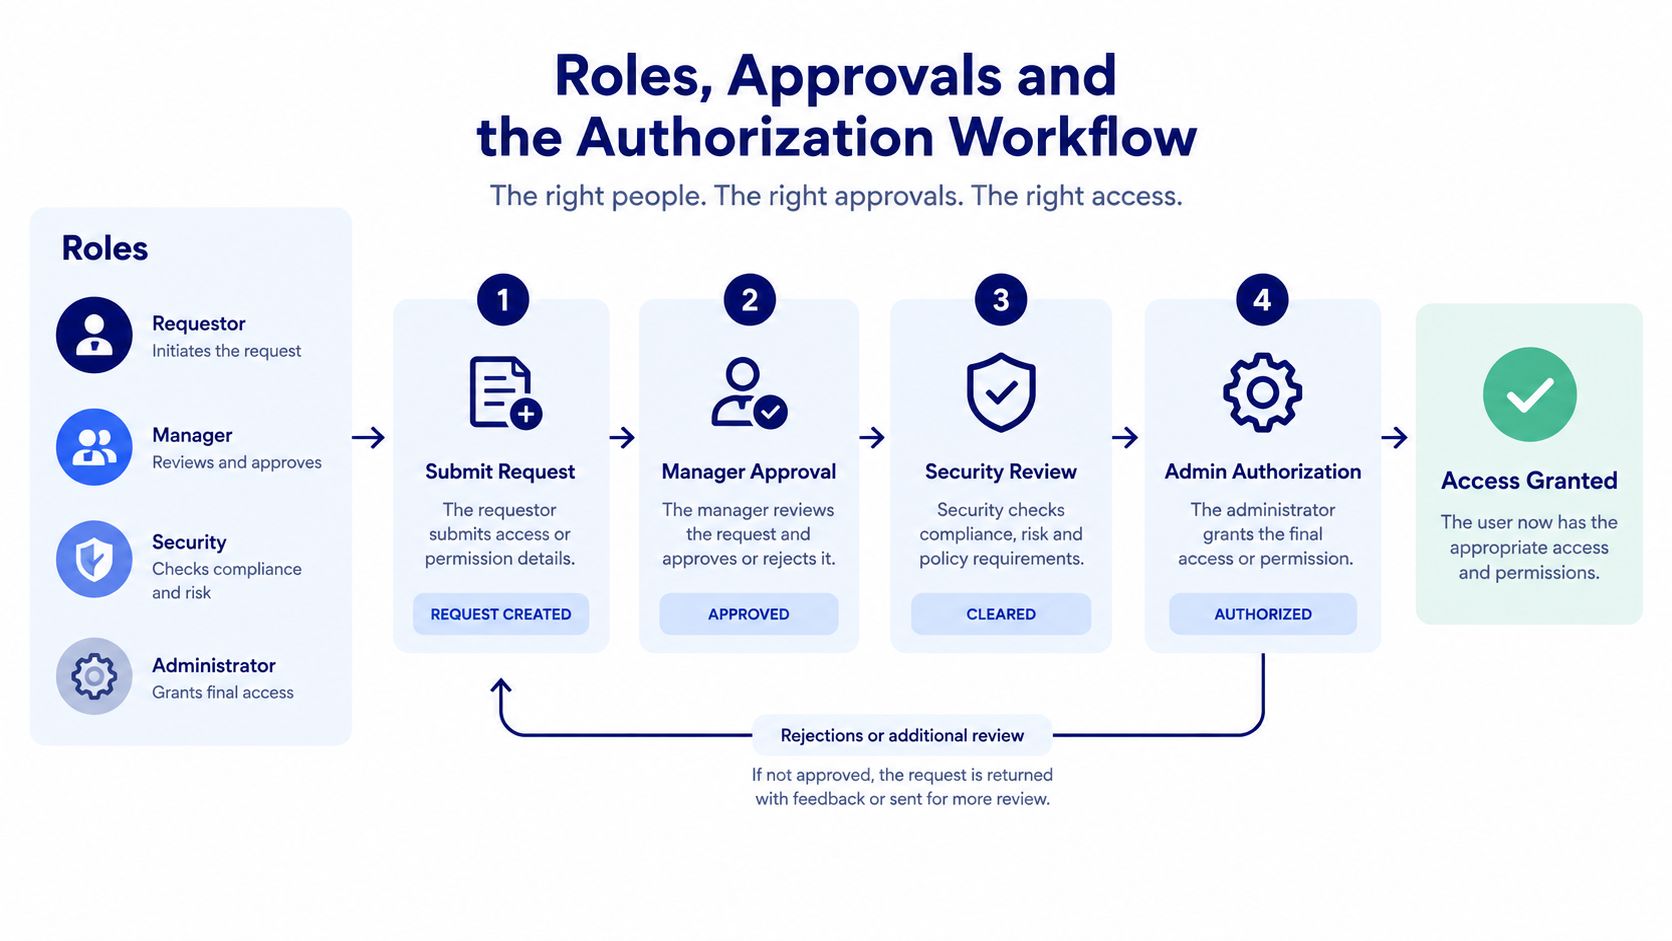
- A named technician requests access for a defined task.
- The appropriate internal owner approves the request.
- The technician authenticates using the intended device and identity method.
- The solution provides the required access to the approved resource.
- An attempt to reach an unapproved resource is denied.
- The organization can observe and intervene in the session as required.
- Temporary authorization expires, and active-session behavior follows policy.
- An authorized reviewer retrieves the associated evidence.
Add scenarios such as a failed connection, an approver who is not available, and an urgent support request. For OT, agree on intervention and recovery steps with the operations owner before testing.
Compare the Full Operating Cost
Look at the full deployment cost. This includes licensing, required components, infrastructure, integrations, recording storage, support, and ongoing admin work.
Do not assume a broad portfolio is complex. Do not assume an agentless solution needs little integration work. The effort depends on your environment and the controls you need.
Frequently Asked Questions
What Is the Best Privileged Access Management Solution for Vendors?
The best solution is the one that meets your vendor-access needs in testing. It should protect credentials and identify each user. It should also limit resource access, enforce approval and expiry, and give you the session oversight you need.
Is Traditional PAM Enough for Third-Party Access?
It can be, if the deployed solution covers the full vendor workflow. A credential vault alone is not enough. Check the external access path, support for unmanaged devices, task-based approval, session controls, and revocation behavior.
Do You Need Both PAM and PRA?
Some PAM platforms include PRA features. Others use separate products or integrations. Before you add another component, check whether your current setup already meets your needs.
Is ZTNA or SASE a Replacement for Vendor Access Controls?
ZTNA and SASE can provide important access and security features. Whether they fit a vendor use case depends on the features you deploy. Check privileged credential handling, session oversight, task-based access, and support for your target systems.
Does Agentless Access Eliminate Vendor Device Risk?
Agentless access reduces the need to install software for supported access methods. It does not remove risks such as compromised endpoints or captured screen content. Strong login checks, resource limits, and data-handling controls still matter.
Can a PAM or PRA Product Guarantee Compliance?
No. A product can support compliance controls and evidence collection. But compliance also depends on your policies, configuration, procedures, and the rules that apply to your organization.
Choose for Secure Third-Party Access
The best privileged access management decision starts with the work your vendors need to do.
Protecting credentials is still essential. But secure third-party access also needs a controlled connection, the right approval, visible activity, and a reliable end to access. That is the job of remote privileged access management.
Safous Privileged Remote Access supports policy-based application access and privileged session controls for IT, OT, and external vendors. Test those capabilities against your own support and maintenance workflows.
Related Resources
Subscribe with Safous
Receive the latest news, events, webcasts and special offers!
Share this
How to Write a Vendor Remote Access Policy: A Practical Template for Secure Third-Party Access
How to Write a Vendor Remote Access Policy: A Practical Template for Secure Third-Party Access
Oct 20, 2026
11
min read
Why Is Managing Third-Party Access Important?
Why Is Managing Third-Party Access Important?
Mar 02, 2023
3
min read
What Is Access Governance? Why Third-Party Access Needs a Different Model
What Is Access Governance? Why Third-Party Access Needs a Different Model
Oct 06, 2026
9
min read